If you have read much of our blog, you have met a whole cast of scams: phishing emails, cloned-voice phone calls, fraudulent texts, trick QR codes, fake gift card requests, bogus tech support pop-ups. They look like different threats, and in their details they are. But underneath, almost all of them are the same thing wearing different costumes. That single thing is called social engineering, and it is the most important idea in cybersecurity that most business owners have never had explained to them.
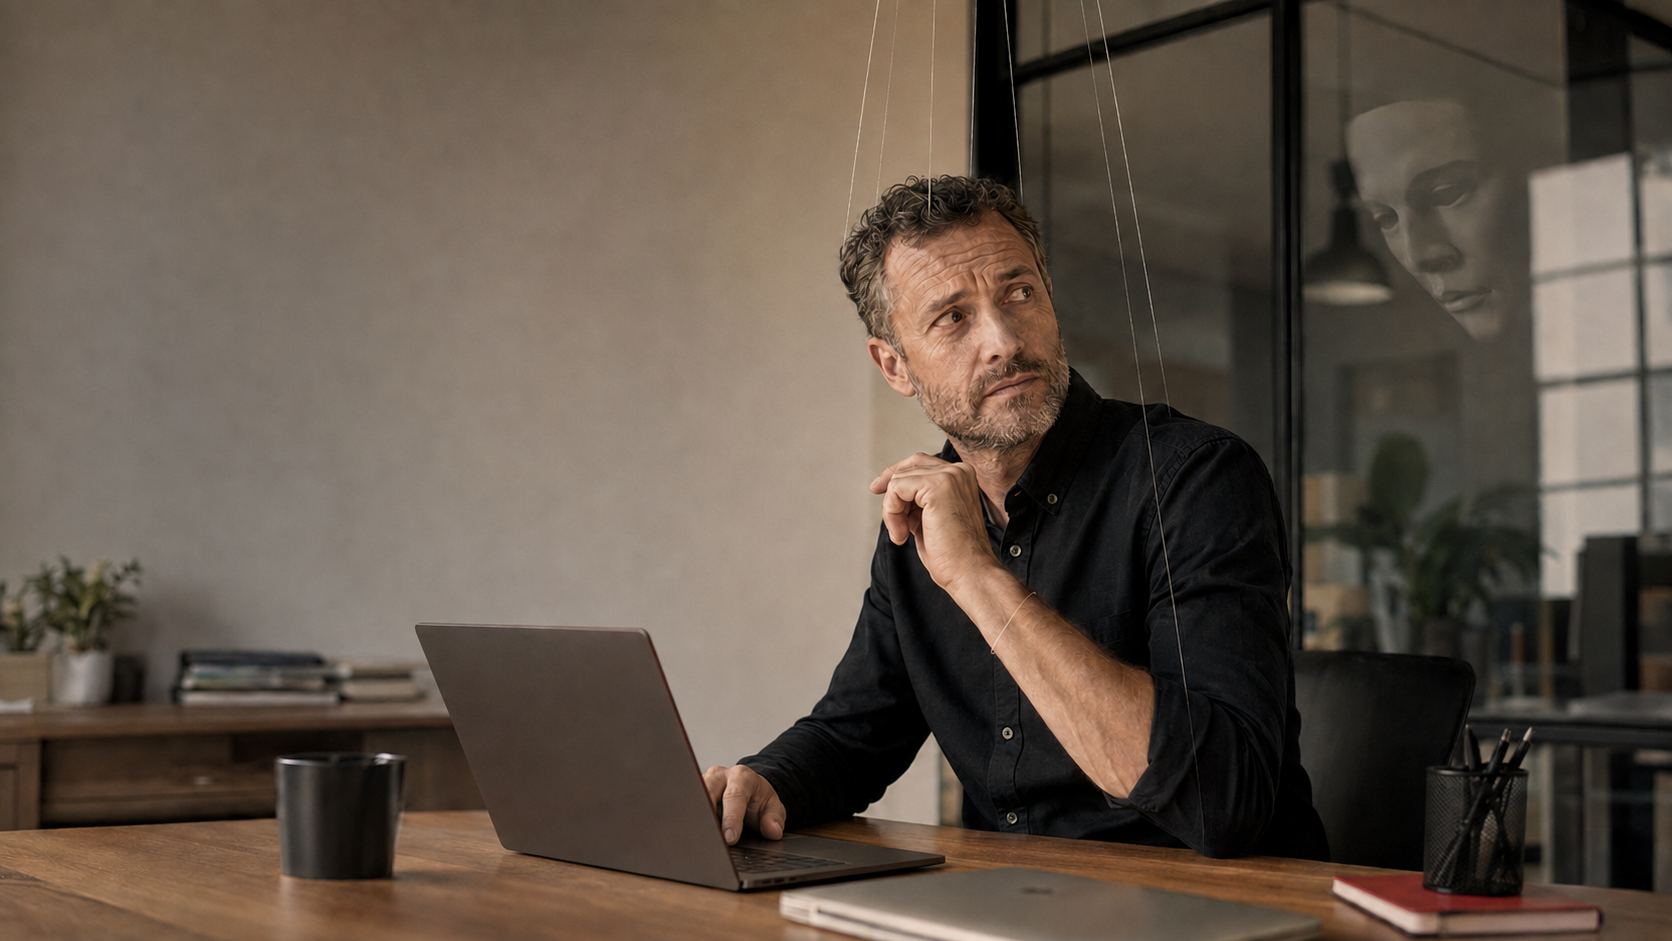
Here is the definition in plain English: social engineering is the art of manipulating people, rather than hacking machines, to get what a criminal wants. It is human hacking. Instead of breaking through your technology, the attacker tricks a person into opening the door for them, giving up a password, sending a payment, clicking a link, or plugging in a device. And because it targets human nature rather than software, it works across every kind of technology and slips past defenses that only guard the machines. Understanding social engineering is like learning the con artist's playbook, because once you can see the moves, you can stop falling for them. Let me show you how it works.
Why social engineering is the real threat
Most people picture cyberattacks as technical: a hacker typing furiously, breaking codes, exploiting some obscure flaw. That happens, but it is not how most businesses actually get hurt. The overwhelming majority of real attacks begin with, or rely entirely on, tricking a person. The criminal does not need to defeat your firewall if they can convince an employee to hand over a password. They do not need to crack your systems if they can persuade your bookkeeper to wire money to the wrong account. The human is the easiest way in, so the human is the target.
This is why social engineering matters so much. You can have excellent technology, and a single well-crafted manipulation of one person can still cause a serious breach. It is also, in a sense, encouraging news, because it means that understanding the trick, and building a few good habits, protects you against a huge swath of threats at once. You do not have to learn a hundred different scams. You have to recognize the handful of psychological moves underneath all of them.
The con artist's playbook: the moves behind every scam
Social engineers, like the con artists of old, rely on a small set of psychological levers. These are the buttons they push to get people to act against their own interest. Learn to notice them, and you will start spotting scams everywhere. Here are the main ones.
Authority. People are wired to comply with those who seem to be in charge. So the scammer pretends to be the boss, an executive, the bank, the government, or a known company, because a request that appears to come from authority gets less scrutiny. The fake email from "the CEO" asking for an urgent payment, the call from "the IRS," the message from "your bank," all lean on authority to lower your guard.
Urgency. Almost every scam manufactures a sense that you must act right now. An account will be closed, a payment is overdue, a deal will fall through, a problem must be fixed immediately. Urgency is the con artist's favorite tool, because hurried people do not think carefully, and thinking carefully is exactly what would expose the scam. Any message pushing you to act fast should make you slow down, not speed up.
Familiarity and trust. Scammers impersonate people and brands you already know, because we extend trust to the familiar. An email that looks like it is from a vendor you work with, a text that seems to come from a coworker, a voice on the phone that sounds like your bookkeeper, all borrow the trust you have already given to someone real, and turn it against you.
Fear. Closely related to urgency, fear short-circuits good judgment. Your computer is infected, your account has been compromised, you are in legal trouble, someone has your data. A frightened person wants to make the scary thing go away, and the scammer offers a quick "solution" that is actually the trap.
There are others, greed and curiosity among them, the promise of a prize, the mystery of a found USB drive, but authority, urgency, familiarity, and fear are the core of the playbook. Notice that none of these have anything to do with technology. They are timeless human levers, the same ones con artists used long before computers existed. The internet just gave them a faster, cheaper way to pull the strings.
The same trick, a hundred disguises
Once you understand the playbook, you will see it behind every specific scam we write about. They are all social engineering, just delivered through different channels.
The phishing email is social engineering by email, using authority and urgency to get a click, and learning to spot it is exactly what we teach in how to train your team to spot a phishing email. The voice cloning scam is social engineering by phone, using familiarity, a trusted voice, and urgency. Fraudulent text messages are social engineering by text. The QR code scam hides the trick in a little square. The gift card scam leans on authority and secrecy. The fake tech support pop-up runs on manufactured fear. The e-signature lure uses routine and trust. Even the found USB drive is social engineering, exploiting simple curiosity. And business email compromise, the costliest of them all, is social engineering aimed straight at your money.
They feel like a dozen separate threats to keep track of. They are really one threat, human manipulation, wearing a dozen masks. That realization is powerful, because it means the defense is largely the same across all of them.
The universal defense
Because social engineering targets people, the defense is fundamentally about people, supported by technology. And the good news is that a single mindset defeats most of it: recognize the manipulation, and verify before you act.
In practice, that means training yourself and your team to feel the psychological levers being pulled. When a message creates urgency, invokes authority, leans on familiarity, or triggers fear, especially around money, passwords, or access, that is the moment to slow down rather than comply. The feeling of pressure is not a reason to act fast; it is a signal to be careful. And then verify through a channel you control: call the person back on a known number, go to the website directly, confirm the request independently rather than trusting the message in front of you. A real request survives verification. A scam falls apart the moment you check. That one habit, verify instead of trust, is the antidote to almost the entire playbook.
Technology plays a vital supporting role. Email security filters out many manipulations before they reach a person. Multi-factor authentication means that even if someone is tricked into giving up a password, it is not enough to get in. Monitoring catches trouble early. But the heart of the defense is a team that knows the con artist's moves and has the confidence to slow down and verify, which is why building that awareness into your culture is one of the highest-value things a business can do.
How we think about it
Social engineering sits at the very center of how we think about protection at Red Door Shield, because it is the common thread behind almost every real attack, and our whole framework, KIT: Keep, Inspect, Trust, is built with it in mind. Keep what is valuable secure, with protections like multi-factor authentication that limit the damage when someone is inevitably tricked. Inspect what is coming in, with the email security and monitoring that catch many manipulations before a human has to judge them. And trust through validation, which is the direct answer to social engineering: you do not extend trust because something feels urgent, authoritative, or familiar, you verify it through a channel you control. We help businesses put both the technology and the human awareness in place, because you cannot patch human nature, but you can prepare people to recognize when it is being used against them.
What ready looks like
Picture your whole team fluent in the con artist's playbook. A message arrives dripping with urgency and authority, and instead of reacting, someone thinks, "this is exactly what a scam feels like," and verifies before acting. A familiar voice makes an unusual request, and it gets a callback to a known number. A frightening pop-up appears, and it gets an eye-roll instead of a phone call. The manipulations that work on the unprepared meet a team that sees the strings being pulled, and they simply do not work.
That is what ready feels like against social engineering. Not hoping no one is ever targeted, everyone is, but knowing your people can recognize the con and have the habit of verifying that makes it fall apart.
Social engineering is the oldest game there is, human manipulation, given new speed and reach by technology, and it is the real engine behind nearly every attack your business will face. But that also means understanding it protects you against nearly all of them at once. Learn the playbook, share it with your team, and build the verify-first habit that defeats it. If you want help building both the human awareness and the technical protections that stand up to social engineering, our free Business Security Assessment is the place to start, and it is a conversation worth having today.
Know Where Your Business Stands
Our free Business Security Assessment gives you a clear, professional picture of your current security posture in less than 10 minutes. No technical knowledge required.
Not sure where your business actually stands?
Take our free Business Security Assessment. In under 10 minutes, you will know exactly where your gaps are and what it would take to close them.
Get My Free Security Assessment